€2.59 Million Fine for Excessive Fingerprint Collection and Invalid Consent
The Croatian data protection authority (the Agency for the Protection of Personal Data) imposed an administrative fine of €2,590,000 on a gambling company after completing supervisory proceedings on its own initiative. The case concerned the processing of players’ biometric data, consent practices, and the transparency of information provided to data subjects.
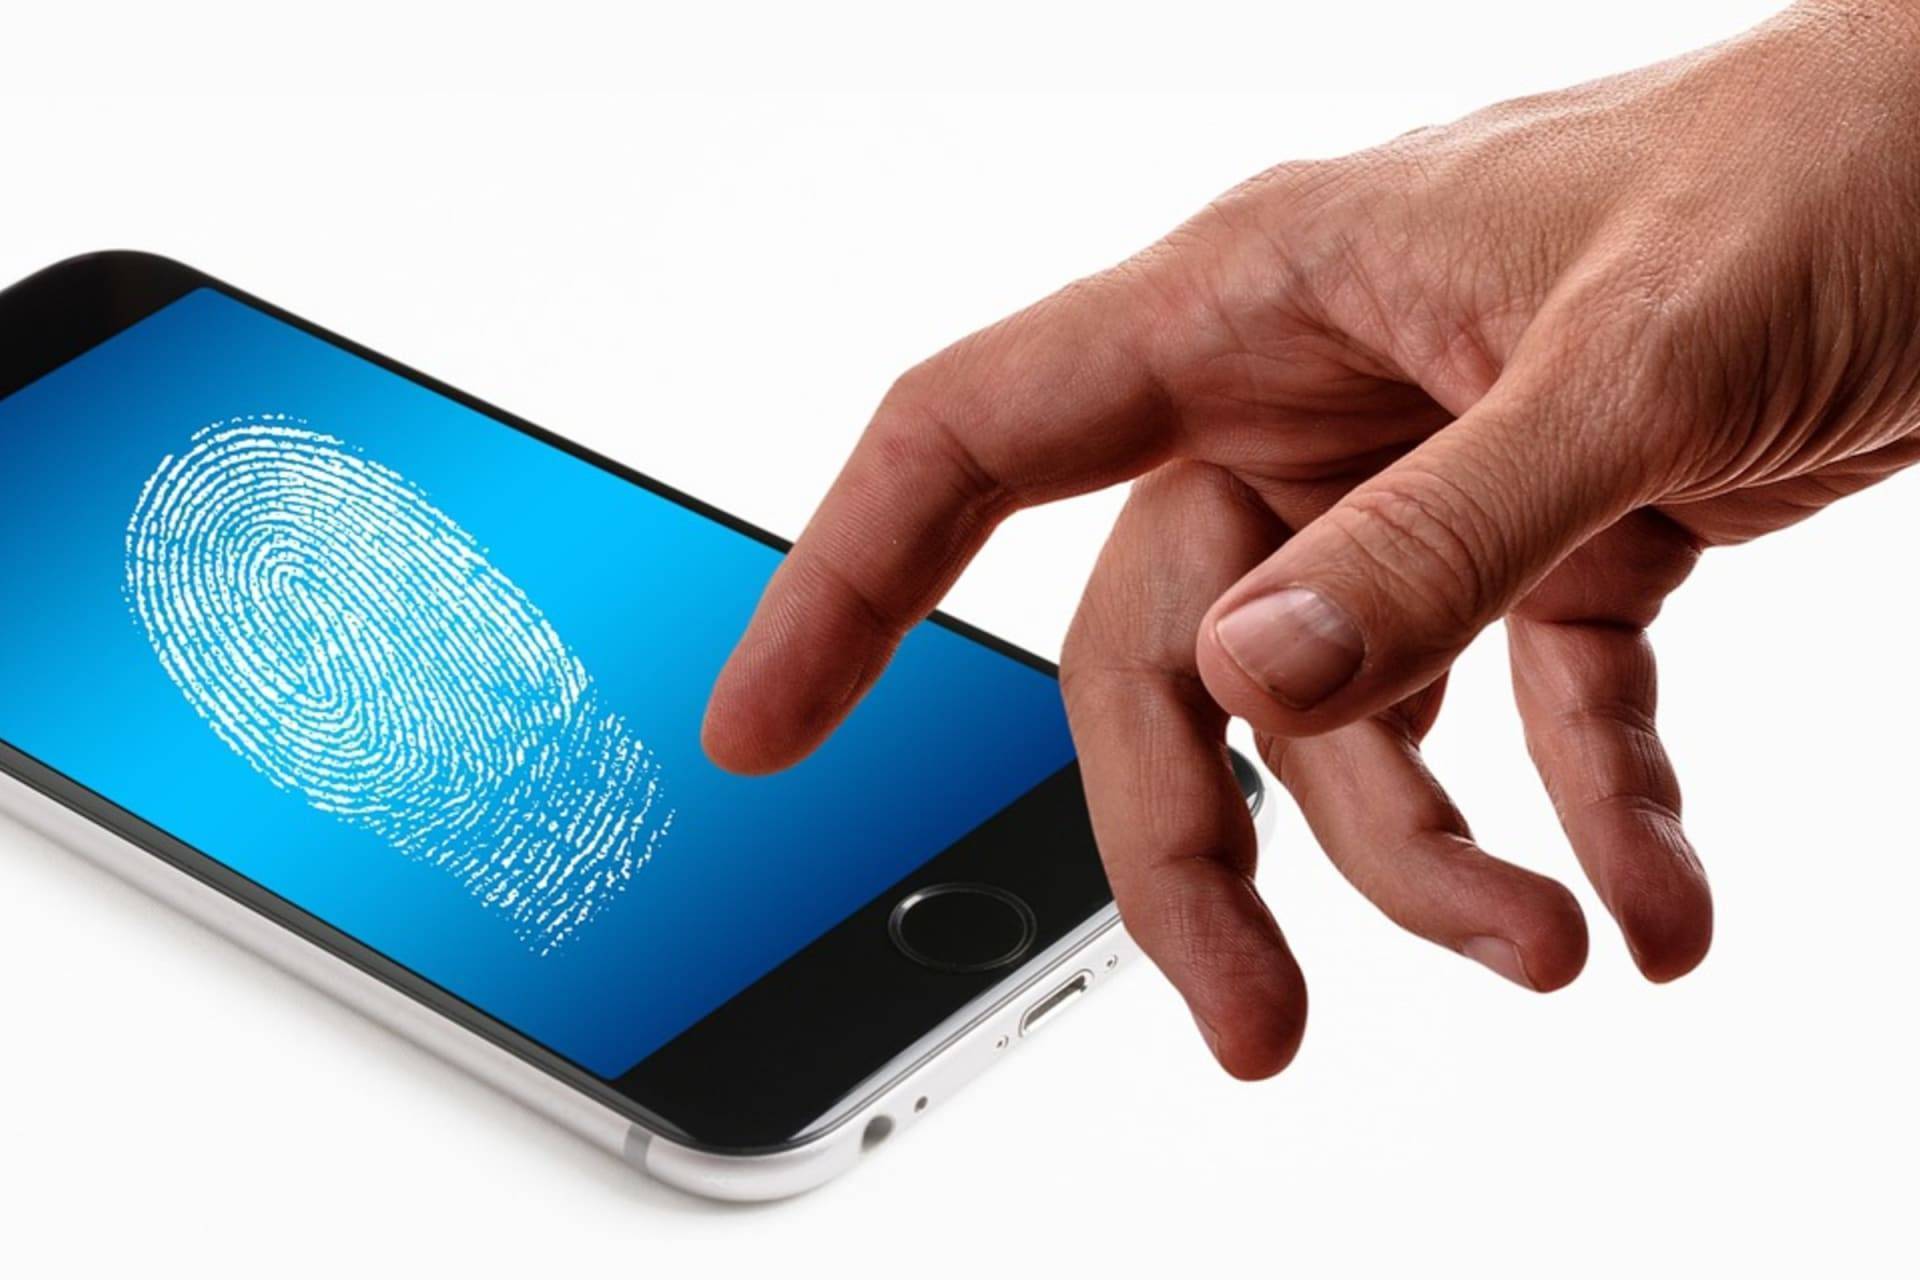
The company allowed players to identify themselves using an RFID chip or fingerprints in addition to an identity card. The inspection found that the company collected and used four fingerprints—two from each hand—for player identification. The controller argued that additional fingerprints were necessary as a backup in case a player’s skin was damaged or a fingerprint could not be read correctly.
However, the authority found that this explanation did not demonstrate why four fingerprints were necessary. Under the GDPR’s data minimization principle, a controller must show that the amount of personal data collected is appropriate, relevant, and limited to what is necessary for the stated purpose. If player identification can be achieved effectively by collecting fewer fingerprints and using additional verification methods, collecting four fingerprints may be excessive.
The authority also emphasized that consent does not automatically make excessive biometric data processing lawful. Under the national law implementing the GDPR, biometric data may be processed for secure identification of service users when the individual gives explicit consent that meets GDPR requirements. That processing must still comply with the principles of legality, fairness, transparency, purpose limitation, and data minimization. In this case, biometric-data consent had been recorded for 34,933 players, but the authority concluded that the processing lacked valid consent and exceeded what was necessary. The findings involved Articles 5, 6, and 9 of the GDPR.
The investigation also found problems with the company’s consent interface. During registration, players were shown interactive fields for four separate consents. The authority determined that the first two consent statements combined several purposes and did not allow players to choose freely and separately between them.
One statement covered the collection and processing of scanned fingerprints for purposes including service provision, contract performance, identity verification, statistical analysis, profiling, service improvement, protection of rights and property, and preventing minors from participating in gambling. The statement did not clearly distinguish mandatory identification processing from optional biometric processing. As a result, players could not make a genuinely separate and informed decision about each purpose.
A similar issue affected the consent statement concerning photographs. It referred to identity verification, protection of rights and property, and preventing minors from gambling, without clearly explaining whether the photograph was used only for identity verification or for additional purposes. The authority concluded that the consent wording did not meet the GDPR requirements for consent to be voluntary, specific, informed, and unambiguous, in breach of Articles 4(11) and 7.
The company also provided incomplete and inconsistent privacy information. Players received several documents containing conflicting descriptions of the purposes and legal bases for processing. For example, the company’s general rules stated that fingerprints could be used not only to control entry into gambling premises but also to protect minors, enable participation in games, operate a rewards program, and support other activities.
According to the authority, the documents did not clearly connect each processing activity with its specific purpose and legal basis. This prevented players from understanding how their personal data was being used and why. The authority therefore found violations of the transparency requirements under Articles 5(1)(a), 12(1), and 13 of the GDPR.
The decision highlights the need for gambling operators and other businesses using biometric identification to carefully assess necessity and proportionality before collecting sensitive data. Controllers should use separate consent requests for separate optional purposes, clearly distinguish consent-based processing from legally required processing, and provide consistent privacy information that explains each purpose and legal basis in plain language.